29 Jan Risk Assessment in DeFi: Comparing Web3 Wallets, Transaction Simulation, and User-Controlled Security
You are about to swap a stablecoin for a newly issued token. The interface shows an attractive exchange rate, the gas estimate looks ordinary, and the transaction appears routine. Yet the approval request may grant a contract permission to spend far more than the amount you intend to trade. In another case, the transaction itself may be legitimate but route through a liquidity pool exposed to extreme slippage, or interact with a protocol whose front end has been compromised. The wallet is not merely a place to store assets; it is the last interpretive layer between human intention and executable blockchain code.
That distinction matters for DeFi users in the United States, where activity often spans multiple chains, decentralized exchanges, lending markets, liquid-staking systems, and bridges. A useful risk assessment therefore compares not only custodial and non-custodial wallets, but also two operating models: a conventional wallet that primarily displays signing requests, and an advanced wallet that attempts to simulate, interpret, and warn about those requests before execution. The second model can reduce important classes of error, but it does not make protocol risk disappear.
The Core Comparison: Passive Signing Versus Informed Signing
A conventional Web3 wallet commonly presents a user with a request to sign data or submit a transaction. It may show the destination address, token amount, network fee, and a technical representation of the call. This model is straightforward and can be perfectly adequate for familiar, low-complexity actions. Its weakness is that blockchains do not naturally express intent in human terms. “Approve,” “deposit,” “permit,” and “execute” can conceal very different consequences depending on the contract, parameters, and wallet permissions involved.
An advanced wallet with transaction simulation adds another layer. Before broadcasting, it can attempt to estimate the resulting state: which assets may leave the wallet, which assets may arrive, what approvals may be created, and whether the call appears likely to revert. This changes the user’s question from “Do I recognize this website?” to “Does the expected state change match what I intended?” That is a sharper security question because many attacks exploit a gap between a familiar interface and an unfamiliar on-chain effect.
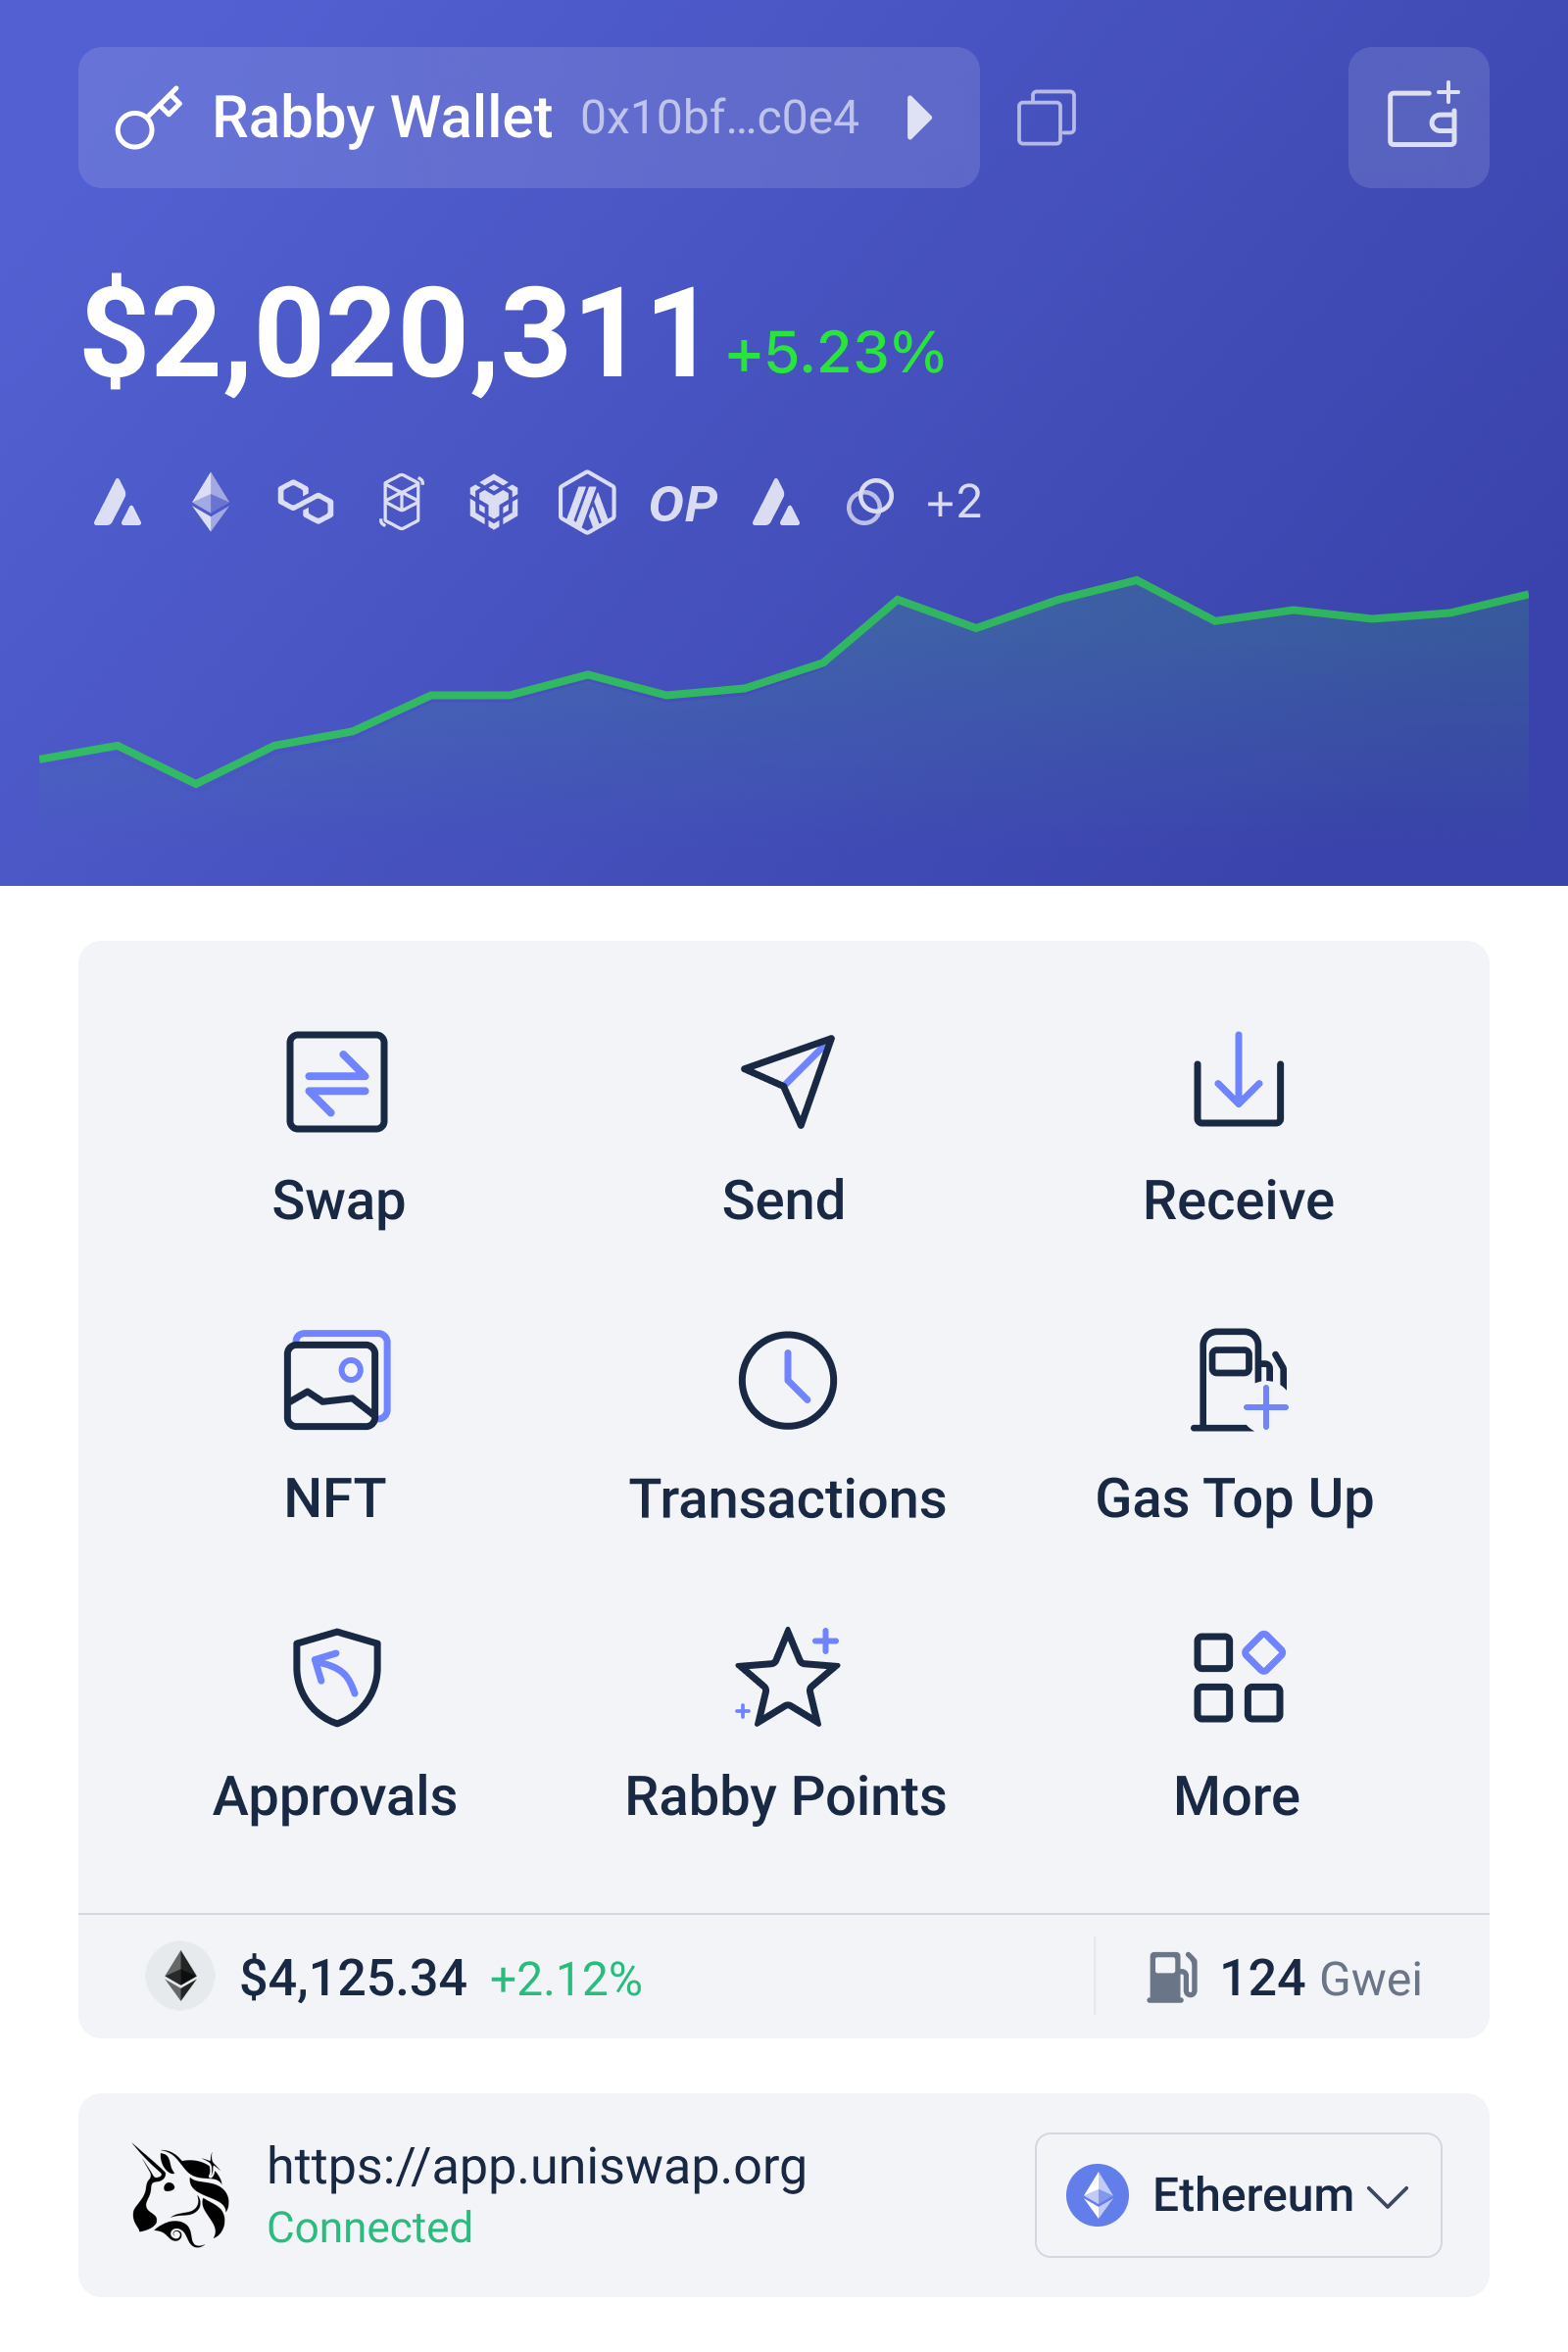
For example, a user may believe they are claiming a reward while the wallet is actually being asked to sign a permission that allows a contract to transfer tokens later. Simulation and transaction decoding can make that mismatch visible. They can also help identify a failed swap before the user pays for a reverted transaction. In practical terms, the wallet becomes a pre-trade control rather than a passive key container. Users interested in reviewing this type of workflow can examine https://rabby-wallet.at/ as a starting point, while still evaluating any wallet according to its actual features, update practices, and trust assumptions.
The comparison is not simply “basic wallet versus safer wallet.” It is better understood as a trade-off between manual interpretation and assisted interpretation. A manual workflow gives experienced users maximum visibility into raw transaction data, but it demands expertise and concentration. An assisted workflow reduces cognitive load by translating contract calls into expected effects, yet the translation itself becomes a component of the security model. If a decoder is incomplete, outdated, or wrong about a contract’s behavior, a clear-looking explanation can create false confidence.
Where the Major Risks Actually Come From
Wallet security is often discussed as if the private key were the entire problem. Key protection is fundamental, but DeFi losses frequently arise after a user voluntarily signs something that has a harmful consequence. The relevant attack surface includes the wallet extension, the operating system, browser sessions, fake domains, malicious token approvals, compromised front ends, poorly designed smart contracts, oracle failures, bridge dependencies, and the user’s own assumptions.
Custody risk and authorization risk
Custody answers who controls the signing key. In a self-custody wallet, the user generally controls the seed phrase or private key, which avoids dependence on an exchange’s withdrawal process or solvency. The corresponding limitation is operational: if the seed phrase is exposed, lost, or entered into a phishing site, there may be no institution able to reverse the event. A hardware wallet can reduce exposure of the key to an internet-connected device, but it cannot prevent a user from approving a malicious contract on the hardware wallet’s screen.
Authorization risk is different. Token approvals and signature-based permissions can allow a spender to move assets under specified conditions. An unlimited approval may be convenient because it avoids repeated confirmations, but it expands the potential loss if the spender contract is abused or its address is not what the user expects. Revoke tools are useful for cleanup, yet revocation is not a substitute for careful approval decisions. A safer habit is to treat every approval as a continuing permission, not as a one-time payment.
Protocol risk and execution risk
Even a correctly decoded transaction can be unsafe because the protocol itself may fail. A lending market can suffer from bad collateral assumptions or an oracle disruption. A liquidity pool can experience price impact that is much larger than expected. A bridge can depend on validators, relayers, or contracts whose failure affects funds across chains. These are not necessarily wallet failures. They are risks of the financial mechanism being used.
Execution risk sits between the wallet and the protocol. Slippage, deadline settings, gas conditions, block reordering, and changing pool reserves can cause the final result to differ from the preview. A simulation is usually a forecast based on current chain state, not a guarantee about the state in the block where the transaction lands. The longer the delay, the more opportunity there is for the result to change. A simulation that succeeds can therefore still be followed by an unfavorable execution, particularly in volatile or thin markets.
What Transaction Simulation Can and Cannot Tell You
Simulation is most valuable when it answers a narrow, concrete question: if this transaction executes against an assumed current state, what balances, permissions, and contract outcomes are likely to result? It can reveal unexpected token transfers, failed calls, suspicious approvals, and interactions with contracts that do not match the website’s description. This is especially helpful for complex transactions that bundle multiple calls, such as a swap followed by a deposit or a claim followed by a transfer.
Its boundary condition is equally important. Simulation does not prove that a protocol is solvent, that its code is free from vulnerabilities, or that a token will retain value. It also cannot reliably convert every arbitrary contract into a complete human explanation. Contracts may use proxies, upgrade mechanisms, external calls, signatures, callbacks, or state-dependent logic. Some threats are deliberately designed to look harmless during an initial review and behave differently after a condition changes.
There is also a conceptual distinction between transaction safety and investment safety. A wallet may accurately show that a trade will exchange one token for another, while saying little about whether the purchased token is liquid, fairly valued, transferable, or governed by trustworthy code. In other words, simulation can improve execution transparency without validating the economic proposition. Users should not mistake “the call does what it says” for “the asset is a good decision.”
Warnings have a similar limitation. A warning system can use address reputation, contract metadata, known patterns, and transaction analysis to identify danger signals. It may be highly useful against common phishing and approval mistakes. But a clean result is not a certification, and a warning does not automatically mean loss is certain. Risk detection is probabilistic and time-sensitive. New contracts, newly compromised websites, and rapidly changing DeFi conditions may not yet be represented in the available data.
A Reusable Risk-Assessment Framework
Before signing, separate the decision into four questions. First, identity: am I connected to the intended domain, chain, account, and contract address? Second, intent: what exact action do I believe I am authorizing? Third, effect: which assets, permissions, and state changes should appear after execution? Fourth, resilience: what happens if the protocol, market, interface, or transaction path behaves unexpectedly?
This framework prevents a common mistake: treating interface familiarity as evidence of safety. A professional-looking website proves very little about the contract receiving the call. Conversely, an unfamiliar interface is not automatically malicious, although unfamiliarity should raise the required level of verification. The wallet’s simulation is most useful when it helps answer the second and third questions, while the user remains responsible for investigating identity and resilience.
For larger positions, a layered process is more appropriate than reliance on one feature. Use a separate wallet for experimentation and high-risk applications; keep long-term holdings away from routine signing activity; prefer limited approvals where practical; confirm the network and recipient; and use a hardware signer when the value at risk justifies the additional friction. Test an unfamiliar protocol with a small amount, but remember that a successful small transaction does not establish that later calls are safe.
There is a genuine usability trade-off here. More warnings, confirmations, and separate accounts can slow down trading and create alert fatigue. If every transaction produces an alarming message, users may begin clicking through warnings without reading them. The best security design is therefore not the one with the greatest number of prompts, but the one that emphasizes meaningful deviations: an unexpected spender, an unusually large approval, a different recipient, a contract upgrade, or a balance change that conflicts with the user’s stated goal.
Comparison by User and Use Case
For a beginner making occasional transactions, a wallet with clear decoding, simulation, and approval visibility is generally preferable to one that presents opaque signing data. The primary benefit is educational as well as defensive: the user can learn how an approval differs from a transfer and how a multi-step DeFi action changes account state. The limitation is that beginners may still over-trust polished explanations and should be encouraged to start with low-value transactions.
For an experienced DeFi trader, speed and composability may matter more. A basic signing flow can be efficient, and expert users may inspect contract data independently. Yet advanced users face a wider attack surface because they interact with more protocols and may hold valuable positions across several chains. Simulation, address screening, and approval management can reduce routine errors, even if they do not replace independent contract and market analysis.
For long-term holders, the best fit may be a deliberately boring setup: minimal approvals, a segregated account, hardware-backed signing, and infrequent interaction with decentralized applications. An advanced wallet can still help by showing whether an occasional transaction has an unexpected effect, but the key risk reduction comes from limiting exposure. Convenience features are most valuable when they support that discipline rather than encourage constant connectivity.
What to Watch as Wallet Security Evolves
If wallet providers improve simulation quality, the important signal will not be the number of warnings displayed. It will be whether users can understand the reason for a warning, distinguish a reversible concern from a severe one, and see what information the analysis does not cover. Better interoperability across chains and more consistent contract decoding could make informed signing easier, but fragmented standards and upgradeable contracts remain structural difficulties.
A plausible near-term direction is a wallet that behaves more like a transaction control center: identifying the intended action, comparing it with the resulting state, tracking persistent permissions, and applying different thresholds based on account purpose. That would be valuable if users retain the ability to inspect raw details and override automation deliberately. It would be dangerous if convenience encouraged users to outsource judgment entirely to a risk score.
Frequently Asked Questions
Does transaction simulation guarantee that a DeFi transaction is safe?
No. It can reveal likely balance changes, permissions, and execution failures under an assumed chain state. It cannot guarantee that a protocol is secure, that a token has value, or that market conditions will remain unchanged before confirmation.
Is a hardware wallet enough for DeFi security?
No. A hardware wallet helps protect the signing key from many device-level attacks, but it does not determine whether the transaction is economically sensible or whether a contract is malicious. The signer still needs to verify the domain, contract, approvals, and expected effects.
What is the most useful habit for reducing wallet risk?
Pause whenever the expected result is unclear. Confirm the chain, contract, recipient, approval amount, and post-transaction balance changes. Separate long-term holdings from experimental DeFi activity, and treat every persistent permission as an ongoing exposure.
The practical conclusion is not that one wallet feature can eliminate DeFi risk. It is that risk assessment improves when the wallet helps translate code into consequences before the user signs. The strongest setup combines that visibility with segregated accounts, controlled approvals, independent verification, and a realistic understanding of protocol and market failure. In DeFi, security begins not at the moment a transaction is rejected, but earlier—when the user asks whether the proposed state change is truly the one they intended.
No Comments